
Prove who entered, who approved them, who escorted them, and when they left.
Audit-ready visitor logs and physical access evidence for federal contractors. Every check-in, screening result, host approval, escort assignment, badge issuance, and review decision is captured in append-only audit logs and exports as evidence for CMMC, NIST SP 800-171, ITAR, EAR, and DFARS reviews.
Append-Only Audit Stream
Events are append-only and linked to stable UUID-backed records.
Human-in-the-loop Decisions
Recorded reviewer decisions and rationale can be reviewed alongside available AI assist context.
Evidence Pack Exports
Export case timelines, decision artifacts, and checksums in one package.
Defense workflow
Track visitor screening, adjudication queue transitions, and policy checkpoints for export-sensitive facilities.
Education workflow
Review tuition payer and party cases with the same append-only event model and evidence exports.
Defense: Visitor screening, adjudication decisions, and export-safe chain of custody.
Open Cases
14
4 escalated
Median Review SLA
41m
last 7 days
Audit Events / 24h
3,824
append-only
D-2048
Visitor: T. Reed
Owner
Alex Thompson
Source
Front Desk Kiosk
Case Age
17m
Append-Only Event Timeline
4 events
Screening triggered
09:14
Checked OFAC, BIS, UN, EU, UK sources during check-in.
Actor: system
Case opened
09:15
Risk score 76 crossed adjudication threshold.
Actor: risk engine
Document review
09:21
Passport and host attestation added to the case evidence set.
Actor: Alex Thompson
Policy checkpoint
09:27
ITAR visitor workflow enforcement validated for Site 03.
Actor: system
Evidence Pack
Generated 09:28
Pack ID
EP-7931
Format
PDF + JSON
Checksum
sha256:8f5ac4b2...f12a
Interactive sample data. Mirrors SecurePoint workflows for defense and education programs.
How the Audit Trail Is Built
Record workflow activity
Recorded screening, queue, decision, and policy events use stable record IDs so reviewers can trace the available history.
Review with human authority
AI can summarize and rank context, but authorized reviewers make the final disposition and rationale for each case.
Follow the visitor case
Review the visitor case alongside its recorded screening, reviewer decisions, and available visit context.
Export defensible evidence packs
Generate audit packages with recorded timelines, decision context, source versions, and file checksums. A checksum checks file integrity; it does not prove that every workflow event was recorded.
Recorded case context
Case timelines include screening source, reviewer actions, and evidence updates in one append-only thread.
Visitor review coverage
Review secure facility visitor cases with screening evidence, decision history, and linked visit context.
Prepare evidence for review
Filter, search, and export recorded case history. Export notes identify missing decision-time provenance and explain the scope of the records included.
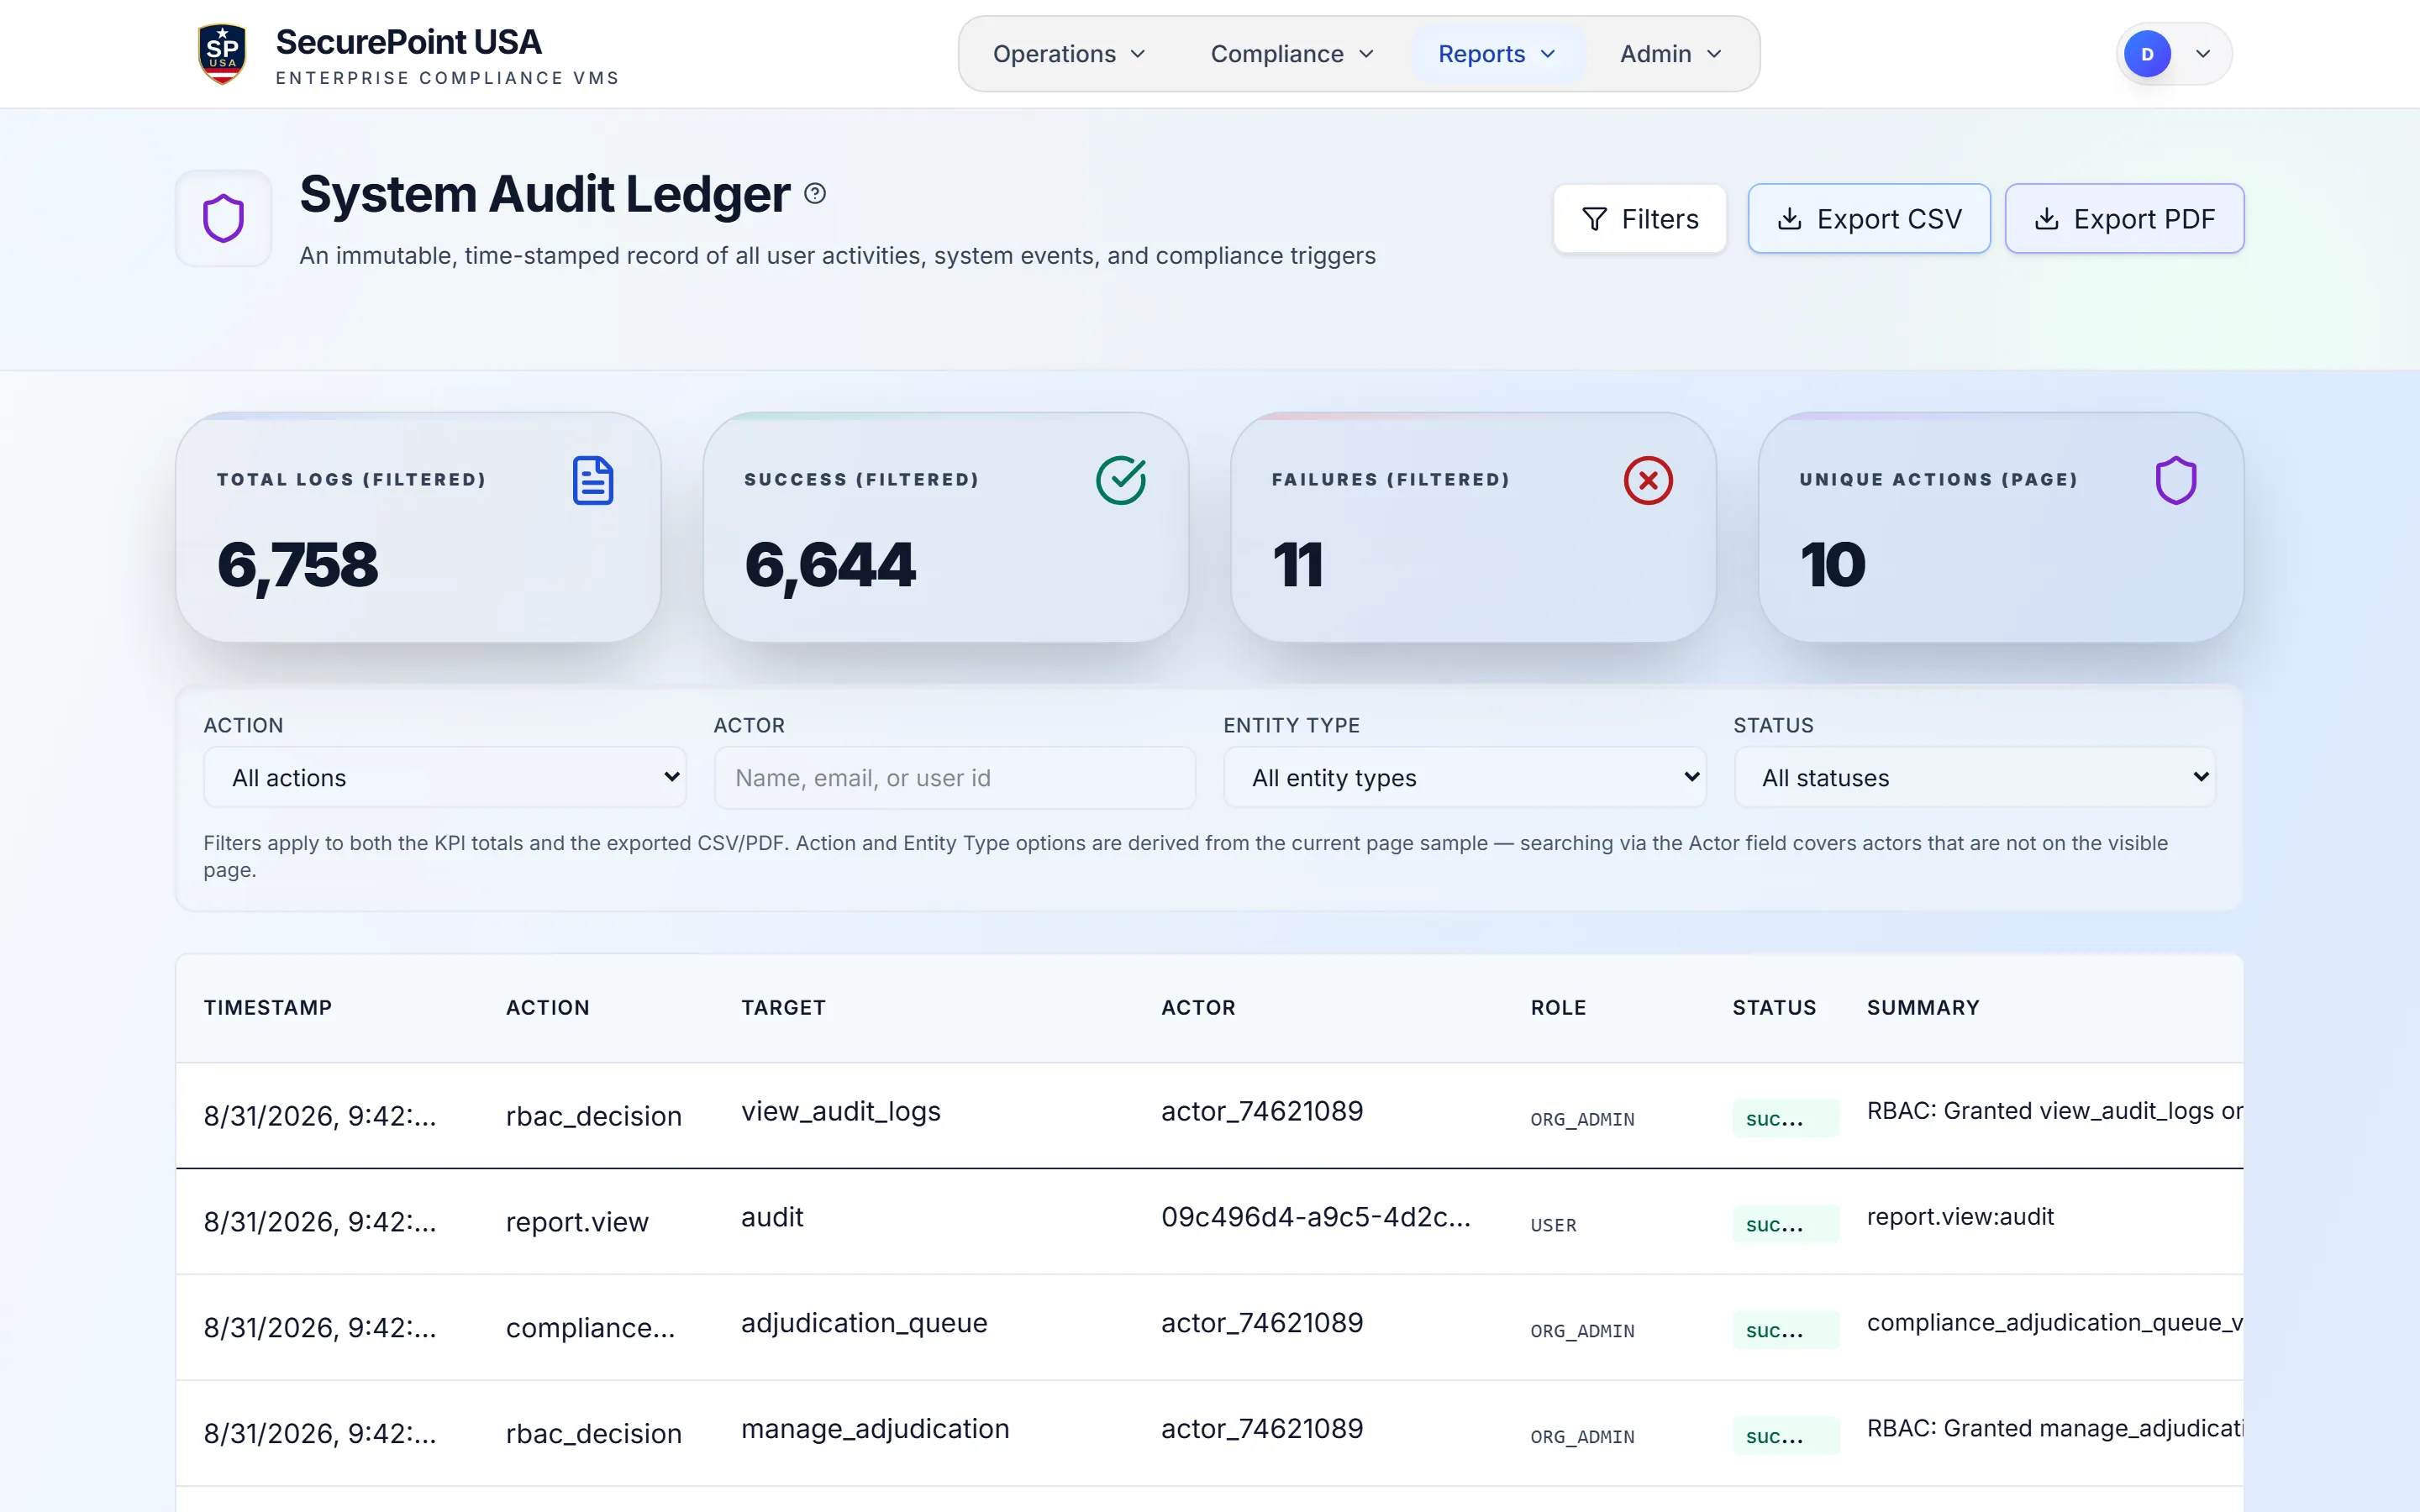
What the audit trail actually looks like
This ledger records user and system activity. Database controls refuse ordinary updates and deletions, and a hash chain checks continuity and the fields it covers. Documented retention and privileged maintenance procedures are separate controls.
Swipe to pan the screen
Read the transcript
When an auditor asks how visitors were screened, an admin opens the Evidence Center and picks a template and a date range.
SecurePoint builds a ZIP file with screening results, review decisions and audit records from that period, and its manifest lists an SHA-256 checksum for each file.
Evidence Pack History keeps each sealed pack, so a later download is the same file, with the same checksum.
The audit ledger shows who did what, and when: check-ins, screening results, reviewer decisions, and exports.
Users can't edit or delete ledger records, and exports from this page come with an SHA-256 checksum.
SecurePoint Visitor. Screen visitors at check-in, and keep the decisions on record.
Physical access evidence for federal contractors
CMMC, NIST SP 800-171, and DFARS reviews ask for the same shape of evidence: who entered, who approved them, who escorted them, where they went, and when they left. SecurePoint produces that evidence as a continuous, append-only record that you can export, not a spreadsheet you have to rebuild before the assessment.
Visitor decision history
Review recorded clear, hold, and deny decisions with their available reviewer, rationale, and screening references. Older records can lack decision-time screening provenance; the export identifies those gaps.
Host approval + escort records
Recorded host approvals, escort assignments, and badge events link to visitor sessions for review alongside check-in and checkout activity.
NIST SP 800-171 PE alignment
The same evidence is direct for PE.L2-3.10.3 (escort visitors and monitor visitor activity) and PE.L2-3.10.4 (maintain audit logs of physical access), and supporting for PE.L2-3.10.1 (limit physical access). An assessor assesses your organization, not a vendor.
Export-ready evidence packs
Exports include timeline, screening source versions, reviewer actions, and checksums so the export itself is verifiable.
See related: CMMC visitor logs, defense contractor visitor management, and ITAR/EAR visitor workflows.
Connected Capabilities
Sanctions Screening
Feed high-risk matches directly into adjudication workflows with preserved source context.
ITAR and EAR Workflows
Preserve policy checkpoints and reviewer actions needed for export control evidence.
After Visit Reports
Review available host and session context alongside adjudication evidence packs.
Audit and adjudication FAQs
What does SecurePoint log for adjudication cases?
SecurePoint logs screening events, queue transitions, reviewer assignments, decisions, and evidence generation with recorded timestamps. Recorded events carry organization and relevant record identifiers for traceability.
What visitor records should a federal contractor keep for CMMC?
A defensible federal contractor visitor record typically includes visitor identity, host approval, escort assignment, restricted-party screening result, the controlled areas the visitor was permitted to enter, and arrival/departure timestamps. SecurePoint captures all of these as one visitor session record with append-only audit logs.
Does NIST SP 800-171 require visitor logs?
NIST SP 800-171 includes Physical Protection (PE) requirements that map to limiting physical access, escorting visitors, maintaining audit logs of physical access, and controlling physical access devices. Visitor logs are the standard way teams produce that evidence. SecurePoint helps document these events; it does not provide certification.
Can defense and education teams use the same audit model?
Yes. Defense visitor workflows and education party screening use the same append-only audit design, so teams can apply a consistent review and evidence-pack process across programs.
How are evidence packs validated?
Evidence packs include checksums and manifest details so exported records can be validated for integrity during internal reviews or external audits.
Does AI make final adjudication decisions?
No. AI is assistive only and can provide summaries or prioritization. Final decisions are made by authorized human reviewers and logged in the audit trail.
Build a Faster, Defensible Audit Response Program
Run defense and education adjudication workflows with append-only logs, linked records, and export-ready evidence packs.